Fast-Lane AI Deployment Architectures That Bypass the Construction IT Backlog
AI agents can reach production in weeks by using existing software instead of custom integrations.
Construction firms can deploy AI into live operations in weeks rather than quarters by changing the deployment architecture with technology already available. UI-layer agents, pre-configured vertical tools, and process-first sequencing each offer a way around custom integration work. The workable fast lane removes unnecessary engineering dependencies while preserving the controls that make a deployment safe to operate.
Why construction operations teams are stuck waiting on IT
An operations leader can have a clear use case, a convincing demo, and a coordinator still doing the same reconciliation by hand months later. The ticket is waiting for a team to have time for integration work, or approval has been denied until security review is done. The task itself may be modest. Yet connecting a scheduling tool to a procurement log can trigger work across legacy project management systems, fragmented BIM data, and field tools that were never configured to work together.
Operations sees a task with clear limits, while IT sees another connection to support, another access path to review, and another deployment that needs time from engineers who have little to spare. A security team that treats every integration as a full compliance review can put a small workflow agent into a multi-quarter queue. Better AI does not shorten that queue. Its length depends on the work required to get the tool into production.
Meanwhile, the cost of waiting extends beyond the coordinator hours lost each week. Firms that move AI into production accumulate better historical data, sharper scheduling models, and faster estimating cycles, which make subsequent deployments cheaper and faster. For the operations leader, the question is therefore not simply whether a tool performs the task, but whether it can reach the working process without requiring a new integration project.
How the IT queue actually forms, and what it is protecting
The IT queue is a governance layer that enforces identity, audit logging, data residency, secrets management, and incident response. Those requirements protect the business from failures that even a good demo cannot reveal. Understanding them separates controls that a fast-lane deployment must satisfy from engineering work that a different architecture can avoid.
Northflank's 2026 enterprise deployment guide places SSO integration first among the non-negotiable controls for enterprise AI coding agents. Every agent session must link to a named human identity so that access reviews, offboarding, and audit trails work. The same guide calls for records of agent file access, shell commands, API calls, and PR creation to go into the enterprise SIEM and stay there for as long as needed. Execution needs its own boundary as well. Agents that execute commands or read files need isolated environments rather than unrestricted access to host systems or sensitive data stores.
Secret scanning, license governance, and incident response runbooks round out the requirements that teams can easily skip when pilots move fast. The guide distinguishes this infrastructure from the AI tool itself and identifies treating tool selection as the deployment decision as a common cause of failure. Bypassing IT without replacing its controls creates a governance deficit that can become visible at the next audit and force the deployment out of service. The alternative sequences deployment differently while retaining its governance requirements. Pre-configured controls, vendor-managed compliance, and UI-layer operation can cut parts of a custom build while keeping the requirements the firm must meet.
The three structural approaches that route around the integration queue
UI-layer agents replace access through an API with pixel, keyboard, and mouse interactions to use software already in place. They use the human user's existing permissions and session instead of requiring a new service account or API key. This removes the API integration ticket while preserving the need for deployment approval. A construction application is an agent that reads a P6 schedule, cross-references a procurement log, and flags mismatches in the existing interface without a data pipeline between the systems.
Pre-configured vertical tools take a different route. Specialist vendors package AI for workflows such as preconstruction, scheduling, and procurement tracking, with connectors, controls, and workflow logic already built in. Deployment becomes more of a procurement decision than an engineering project because security teams can review documented, repeatable controls. The “Digital Interns” model applies this approach to discrete preconstruction tasks, including ingesting bid requests, checking plans for code compliance, and generating estimates from historical data. Zacua Ventures' 2026 construction AI report identifies the enabling combination as bounded, context-aware agents and platformization that propagates design changes through quantities, procurement, and field execution.
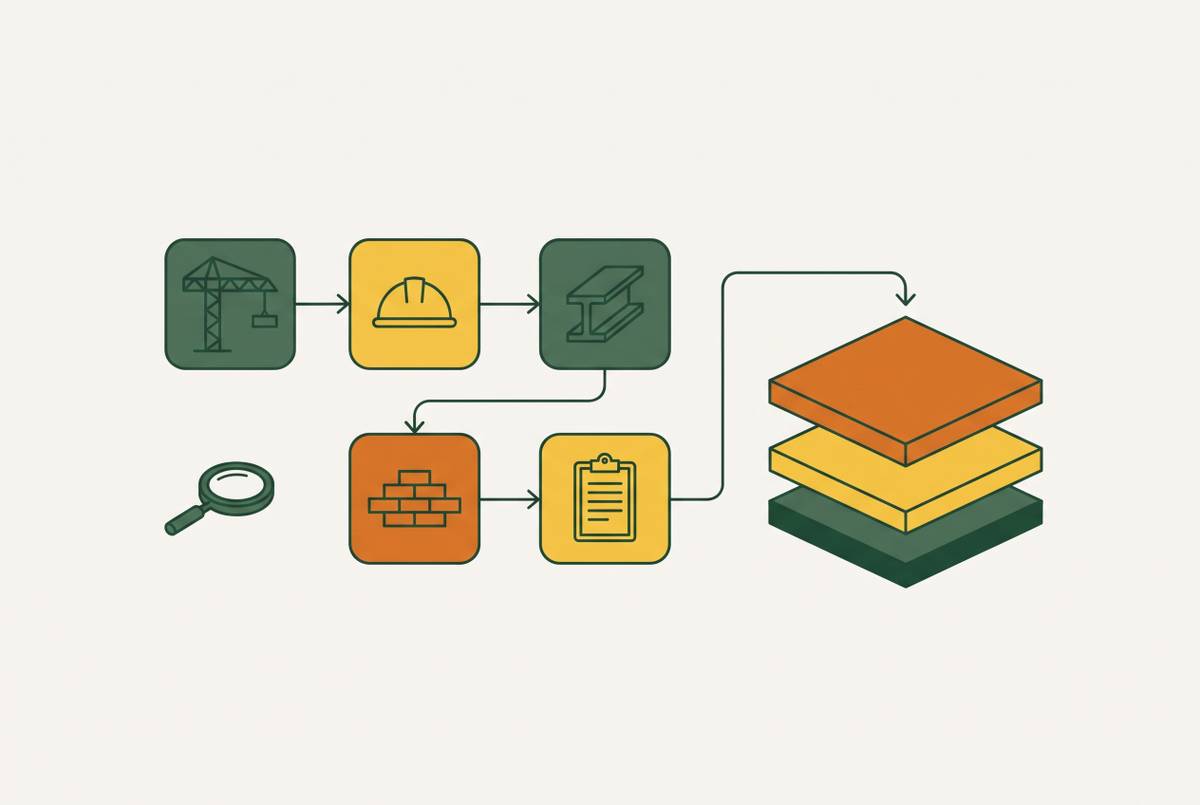
Process-first sequencing changes the unit of deployment. Rather than choose a platform for operations as a whole, the firm selects one painful, high-frequency workflow and limits the initial deployment to it. Fewer systems and data connections create a smaller attack surface and a more bounded security review. As a scope architecture, process-first sequencing can shape either of the other approaches, while providing a route for a narrow custom or lightly configured deployment when the firm's process does not fit a standard product.
What each architecture actually trades away
UI-layer agents are quick to integrate but give up native auditability and a stable interface. Their actions are not logged as API activity, so the firm must instrument the agent execution layer with logging and appropriate access controls and isolation. A screen is also a fragile dependency. When the underlying tool changes its interface, the agent's interaction pattern can break silently, with no API version contract to signal the change. The failure may show up when the agent is in use instead of in staging, and useful screen-level work will feed downstream systems as structured output only if that capability is built in.
Pre-configured tools exchange flexibility for speed because the firm's data must fit the vendor's schema. Proprietary cost codes, unusual subcontractor structures, and non-standard workflows can go beyond what the configuration can handle. The firm then faces a concrete choice. It can standardize the data, potentially taking months, accept degraded output quality, or introduce customization that brings integration work back. When the vendor manages data residency and compliance, the firm also has to rely on how well that vendor meets the rules during regulatory review, and when the vendor owns the workflow logic, process changes have to wait for its release cycle.
Process-first sequencing gives up breadth to preserve a clean boundary. The first deployment does little for work across workflows, and larger gains depend on the firm approving and backing later deployments. Success can itself create pressure to expand. If the firm adds systems, decisions, and exceptions before the governance infrastructure is ready, the narrow deployment becomes the broad integration project it was meant to avoid. These costs become visible at different moments, whether during an interface update, a schema mismatch, an audit, or an expansion beyond the original scope.
Why the process audit has to come before the architecture decision
A fast-lane deployment can get stuck even when the architecture fits the software perfectly. The process may already be broken, and an agent merely makes the failure faster and more visible. Construction workflows often contain undocumented branches, informal exception handling, and coordination conducted through email or verbal agreement. The written procedure is not the whole process. An agent following it cannot account for decisions that never enter the workflow it can see.
The gap is between recorded activity and operative judgment. A stale schedule or an undocumented field decision can make the available record a poor guide to what should happen next. Choosing a more capable agent does not resolve that gap. Neither does replacing a UI interaction with a packaged connector.
A process audit exposes where a coordinator actually makes a judgment call, where data quality breaks down, and which step has the greatest effect on downstream outcomes. A process that stays within a tool already in use may suit a UI-layer agent, while a standard construction workflow may suit a vertical product. When a firm has its own rules for how work gets done, a narrow custom deployment under process-first sequencing may fit. The audit is therefore not an added consulting delay, but the work that removes false starts from a weeks-not-quarters deployment path.
Where fast-lane architectures hit their limit — the physical constraint layer
For construction firms delivering data center, infrastructure, or energy projects, faster AI deployment does not remove procurement, energization, or regulatory constraints. These belong to a different class of problem. The data center buildout makes the distinction especially clear because long-lead electrical equipment can govern delivery on timelines measured in years.
A data center schedule that reflects the work must show separate milestones for utility application, load study, facility study, and service agreement. It must also distinguish equipment order, factory acceptance testing, delivery, installation, energization, and commissioning. A blended energization date hides the dependencies between them. Missing a submittal approval window for medium-voltage switchgear can mean losing a factory slot and slipping energization by a full production cycle. For owners with phased handover or availability credit structures, that slip affects revenue and goes beyond a small change to the schedule.
An agent can flag an at-risk submittal before the factory slot is lost, but only if the workflow contains the relevant milestones and current data. Otherwise, it produces confident output about a broken plan. ABC's May 2026 backlog data shows that data center work disproportionately benefits larger contractors, which also have the operational sophistication to manage long-lead procurement and energization sequences. Smaller contractors need more than deployment architecture to catch up with those skills. For the operations leader, the boundary is between getting risk analysis into the workflow and supplying the field evidence and procurement tracking that make the analysis dependable.
How can construction teams get a first AI workflow live in weeks?
The starting decision should match the process, data readiness, and governance posture of the firm now, rather than identify an architecture that is best in general. First, assess whether the process runs primarily inside one existing tool. If it does, a UI-layer agent can avoid integration work, provided the interface is stable enough and agent-level logging is available. Speed depends on those conditions being true. A familiar application does not by itself make an agent ready for production.
Second, assess whether the work maps onto a standard construction workflow such as preconstruction, bid leveling, schedule risk, or procurement tracking. If so, a pre-configured vertical tool is likely the fastest path when the firm's data meets its schema requirements. Third, assess whether the process depends on unusual cost structures, proprietary sequencing logic, or non-standard subcontractor coordination. That points toward process-first sequencing with a narrow custom deployment. Each answer identifies a deployment boundary as well as an approach.
Before go-live, the team should treat SSO, audit logging, and sandbox isolation for agents executing commands as pre-deployment requirements. The Northflank guide outlines infrastructure with which a prepared team can satisfy those requirements in days. The first process should be painful enough to show visible operational improvement within the first two weeks and narrow enough that failure remains recoverable without a major incident. Scope is the practical safeguard here. A broad transformation roadmap or tool-selection exercise begun before the process is understood recreates the queue on the operations side.
The concrete step this week is to identify the process consuming the most coordinator time and show how it runs today, including the judgment calls and exceptions absent from its written procedure. That demonstration should show whether the work is mostly interface-bound, standard enough for a vertical tool, or based on how that firm alone works. This is the minimum viable process audit. It gives the team a bounded workflow to deploy rather than another platform proposal waiting for approval.